
Rubrik enhances DevOps Protection to preserve legitimate work during recovery
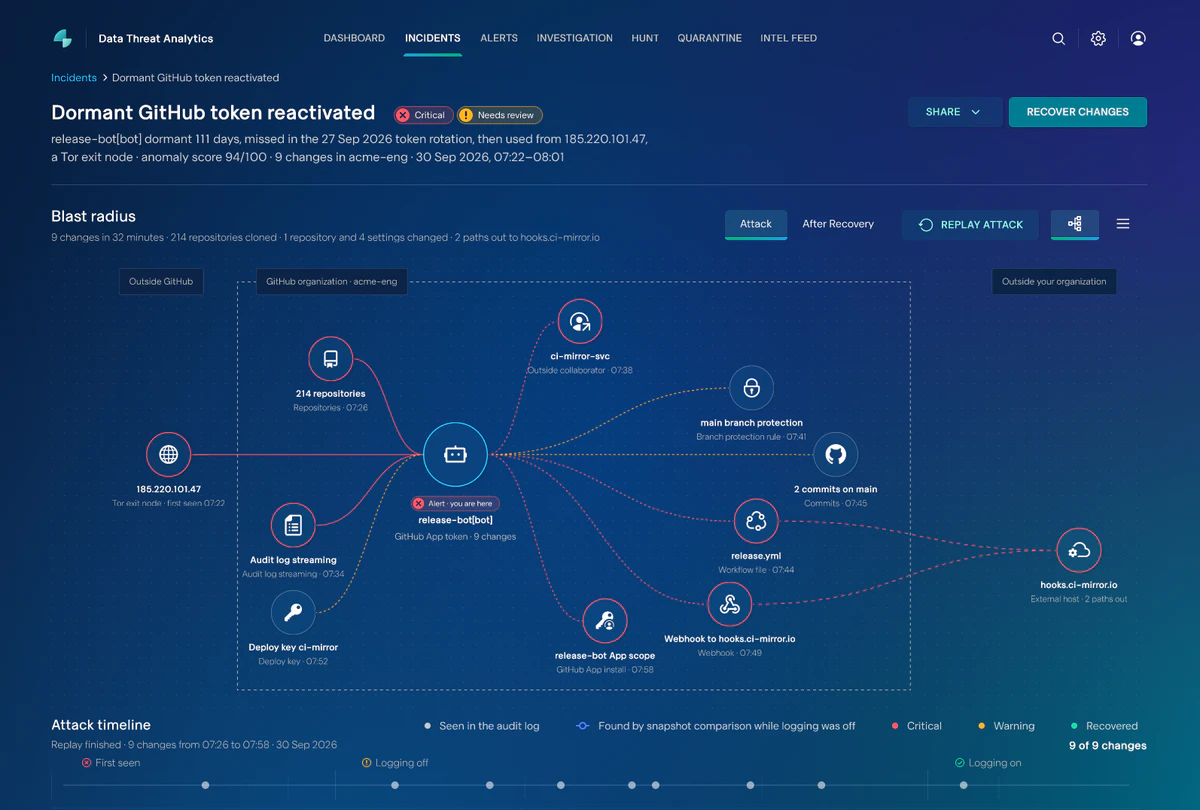
Rubrik has announced cyber recovery capabilities for DevOps platforms Microsoft Azure DevOps and GitHub. With built-in anomaly detection, blast radius investigation, and surgical recovery, organizations will be able to detect suspicious activity on their code, instantly scope the impact of an attack, and undo the attackers’ changes from air-gapped, immutable backups, without disrupting legitimate developer work.
“An organization’s source code is where innovation lives, and attackers know it,” said Anneka Gupta, Chief Product Officer at Rubrik. “One stolen token or poisoned dependency can impact thousands of repositories before anyone notices. Our new cyber recovery capabilities for DevOps allow organizations to detect suspicious activity, see what was impacted, and recover only the unwanted changes, using the air-gapped backups they already trust Rubrik to protect.”
Attackers no longer need to breach perimeters; instead, they compromise legitimate credentials to launch attacks that mimic normal developer activity. Accelerated by AI, these attacks can rapidly spread malicious code across thousands of repositories.
According to Gartner, “a growing number of software engineering leaders are modernizing their DevSecOps toolchains by adopting DevSecOps platforms.” These platforms house an organization’s most critical intellectual property, including source code, CI/CD pipelines, and infrastructure as code. As such, they’ve become a primary, identity-driven attack surface.
Enhanced DevOps Protection capabilities
Operating natively within Rubrik Security Cloud, DevOps Protection Enterprise Edition now connects detection, investigation, and recovery in a single workflow:
- Anomaly detection: Continuously baselines GitHub and Azure DevOps audit logs, correlating them with Rubrik backup metadata to flag suspicious identity activity and produce a prioritized alert that can be routed directly into existing security and ticketing workflows.
- Blast radius investigation: Produces a categorized view of affected assets across repositories, commits, pipelines, workflows, pull requests, and settings, providing the exact scope of impact and determining precisely what needs to be restored.
- Surgical recovery: Recovers only what the attacker changed while preserving legitimate work from other developers, using the clean, air-gapped, immutable backups customers already hold with Rubrik DevOps Protection. Teams will be able to avoid manual rebuilds and organization-wide code freezes.
Expanded developer collaboration stack protection
To ensure complete recovery context, Rubrik DevOps Protection (Foundation Edition) now backs up broader platform metadata, settings, and the developer collaboration stack across Azure DevOps and GitHub. From issues, pull requests, and Azure Boards to wikis, packages, and organization settings, businesses can recover the full context of how their teams build software, rather than just the underlying code.
Rubrik’s cyber recovery capabilities for DevOps platforms Microsoft Azure DevOps and GitHub is expected to be generally available in the coming months.
