Postman Passport controls API access without exposing credentials
Postman has announced the general availability of Passport by Postman, marking the company’s expansion into API security with a standalone product that gives organizations a secure way to consume APIs as human and non-human identities increasingly work side by side.
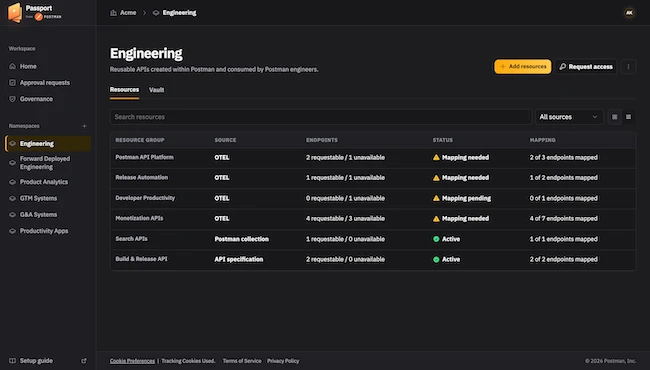
The new product keeps real API credentials inside customers’ environments while giving security teams full attribution for every call, granular control over access, and the ability to revoke access in seconds.
Developers and AI agents need to call APIs constantly, but the credentials that authenticate those calls, API keys, tokens, and secrets, are historically a challenge to control. Once a real credential lands on a developer’s machine, it can quickly spread across .env files, repositories, chat tools, IDE configurations, and CI logs, making it difficult for security teams to fully audit or manage.
A single leaked credential can be used thousands of times before the security issue is caught and resolved, and as AI agents begin calling APIs at 1,000x the rate humans do, the attack surface is widening faster than ever before.
“AI agents get their abilities through APIs, making secure access to those APIs more critical than ever,” said Abhinav Asthana, CEO of Postman. “As developers and AI agents multiply the number of API calls being made, the number of credentials in circulation is growing just as quickly. Passport provides a secretless approach to API access, allowing any human or non-human identity to call approved APIs without ever holding the real credential.”
Passport provides secretless access to SaaS platforms and enables developers, machines, and AI agents to discover and call approved APIs through governed, auditable identities, without ever touching a real credential. Unlike traditional API key management and gateway approaches that focus on distributing and protecting secrets, Passport keeps credentials self-hosted inside customers’ environments.
Key capabilities include:
- Secretless by design: Keeps real secrets inside your cloud and your secret store. Developers and agents receive a secret reference, a cryptographic pointer that is inert without the proxy and bound to the identity that requested it.
- Grant precisely: Grant permission down to the exact action, host, and path you want to allow. Every request is checked against these rules before it ever reaches your vault, so access stays exactly as intended.
- Built for agents: Treats developers and agents identically. Agents receive ephemeral, task-scoped identities minted from a durable parent, enabling organizations to run fleets of agents without distributing long-lived secrets. Sub-agents inherit only a subset of their parent’s permissions.