Transcend Rails brings policy enforcement and spending controls to AI agents
Transcend has launched Transcend Rails, a new category of agent management that goes beyond identity and access control to govern what an agent does.
Every enterprise scaling AI agents hits the same wall: the board asks what agents did last quarter, and no one can reconstruct it. Or an agent deletes, exports, browses, or spends something it shouldn’t, while the only instruction to stop it sits ignored in a prompt. Gartner predicts that by 2030, half of AI agent deployment failures will be caused by insufficient runtime enforcement from AI governance platforms. The result is a trade-off nobody wants: agents kept in a sandbox are safe but produce little, while agents released without controls are one bad action away from a shutdown.
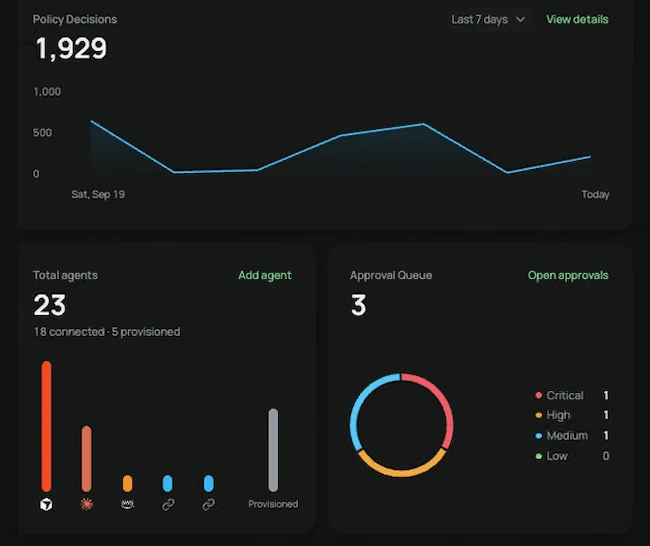
Identity tools establish who an agent is. Gateways decide which systems it can reach. Governance platforms record what it should do. But none can say what an agent is allowed to do once it’s inside. Only Transcend Rails answers “Can my agent do this, for this purpose, right now?” in milliseconds and action-by-action, using the identity, security, and policy data an enterprise already has. Business leaders write the rules once, in plain language, and every agent on any stack runs inside them, with an accountable owner, a complete audit trail, and a kill switch.
“Transcend Rails gives each agent exactly the permissions and the budget its job needs, and nothing more. The ability to encode any business policy, with full ownership and auditability gives me the confidence to scale live agents across my tech stack. The spend controls alone pay for the platform,” said Jess Webster Francis, Associate Director of Cybersecurity, Privacy & AI Governance at Dr. Squatch.
Rails runs on Transcend’s data decision infrastructure, the same engine that already makes 174 billion data decisions and governs 418 million operations and agents inside Fortune 500 systems. It is live across Claude Desktop, Claude Code, and Cursor sessions, including Transcend’s own engineering team’s, plus agents built on AWS Bedrock and AgentCore, Snowflake Cortex, Adobe Experience Platform, and custom builds on any stack, with per-agent budgets and guardian agents that supervise other agents under the same policy.
“The fastest way to get AI agents into production is to make sure they only do what you’ve approved, and that’s what Transcend Rails does,” said Ben Brook, CEO of Transcend. “Businesses spent decades amassing data, and agents are now its primary consumer, running more data use cases than ever, which is why Rails has to be the data context engine that makes the autonomous enterprise possible.”
“Most vendors in this market started from identity, networking access control, or documentation and are adding enforcement. As a data privacy context engine, we started from enforcement in the data path, applying purpose limitation, consent, and regulatory rules inside Fortune 500 infrastructure for nearly a decade,” said Mike Farrell, CTO of Transcend.
“Deciding whether an agent can reach a system is the easy part. Deciding what it may do there, for which purpose and with whose data, is the hard part, which we have solved.”
Rails runs on the same policy brain as Transcend Policy Engine, which already answers “Can I use this data?” across the enterprise, through Sombra, Transcend’s zero-trust security gateway, inside the customer’s own environment. Transcend never touches the API keys or sees the data it governs. Together, the data an agent touches and the action it takes are now governed by one decision.