Sophos uses agentic AI to show businesses which security fixes deserve funding
Sophos has launched Sophos CISO Advantage, an agentic AI-enabled solution that connects security operations to security strategy. The solution gives organizations a picture of their cyber risk, a prioritized plan to reduce it, and measurable proof of progress, in plain language that business leaders can understand, fund, and act on.
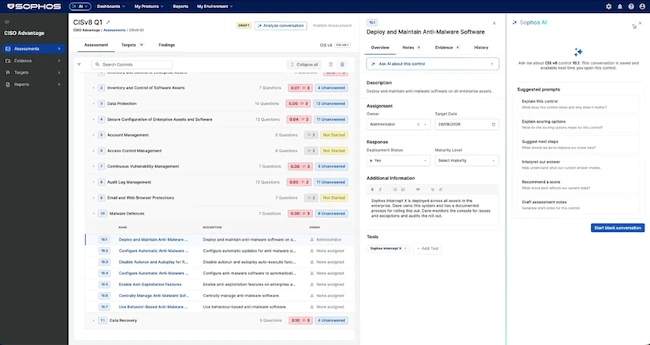
Sophos CISO Advantage defines a new category in the market, turning security data into strategy and measurable improvement, driven by agentic AI. The offering assesses an organization’s environment, maps it against industry frameworks, and turns the result into a prioritized plan at a speed and scale that human experts alone cannot reach.
For most organizations, creating and executing against a strong cybersecurity strategy is both the greatest opportunity and the greatest challenge in strengthening their resilience. The cybersecurity industry has invested heavily in tools that prevent, detect, and respond, with global spending on information security expected to reach $240 billion in 2026.
However, despite significant investment in cybersecurity tools, the market remains fragmented. Organizations often rely on disconnected assessments, spreadsheets, and point solutions to understand and manage cyber risk, making it difficult to measure progress, prioritize investments, and demonstrate the impact of cybersecurity programs.
The gap, in large part, is due to a scarcity in security leadership and talent. According to the 2026 CISO Report, an estimated 35,000 CISOs serve 359 million businesses worldwide, a ratio of roughly 10,000 to one. Hiring alone cannot close the gap. In fact, our 2026 MSP Perspectives Report found that on average, 46% of customers look to their MSP to act as their CISO now; with 84% of MSPs expecting the demand for CISO services to increase over the next year.
Organizations without a CISO lack the skillset and resources to assess risk and build a strategy. Organizations with a CISO are increasingly asked to prove control effectiveness and demonstrate progress to boards, regulators, and insurers, even as the role strains under pressure, as average tenure of a CISO runs 18 to 26 months and 75% are considering a job change.
Sophos CISO Advantage closes that gap. It builds a security assessment unique to each organization’s environment and threat profile, maps controls against frameworks including NIST CSF, CIS v8, Cyber Essentials Plus, and NCSC CAF, and turns the results into a prioritized, budget-aligned roadmap of what to fix first, what it costs, and why it matters to the business. Because it is part of Sophos Fusion, every assessment is informed by live threat intelligence and the collective insight from 625,000+ Sophos-defended organizations, rather than generic benchmarks.
“Good security strategy has always required expertise that’s too scarce to scale, so it’s stayed a luxury only the largest enterprises could afford,” said Rob Harrison, SVP, Product Management, Sophos. “Sophos CISO Advantage changes that. We built it around the question every board is now asking its security team: are we safer than we were last quarter, and can you prove it? Putting a credible answer within reach of any organization, not just the ones that can staff a large security team, is how the industry starts to close the resilience gap.”
Every organization’s path to strengthening their security strategy with Sophos CISO Advantage is different. Some want to own and run the program themselves, with their internal team driving strategy and using Sophos CISO Advantage as their system of record. Others may start with an MSP partner to stand up the program, build confidence, and then transition to running it in-house. Many will start with a baseline assessment of their program, and move into a continuous managed service delivered entirely through a trusted partner. Sophos CISO Advantage is designed to support all three.
For the growing number of MSPs already acting as the de facto security leader for their customers4, it turns that role into a structured, scalable, and billable service. For organizations that want to own their program directly, it provides the system, the framework, and the AI-powered workflows to do it without a dedicated security team. Whichever path fits the business, Sophos CISO Advantage delivers the same outcome: a clear program, measurable improvement, and reporting that leadership can act on.
“CISOs are being asked to move faster, manage more risk, and show meaningful progress to boards, regulators, and insurers. There are too many tools out there that track activity without any insight. What security leaders need now is a solution that helps them understand where they stand, take action, and clearly show how their security posture is improving. The vendors that can bring that together in one AI-native system, from assessment through remediation, will be the ones that shape where this market goes next,” Phil Harris, Research Director, Governance, Risk And Compliance Solutions, IDC, concluded.