
Ransomware gang talked AI agents into doing much of its dirty work
The group behind the Aur0ra ransomware has been using AI agents to move through victim networks, collect credentials and work its way up to domain administrator access, …

Sophos uses agentic AI to show businesses which security fixes deserve funding
Sophos has launched Sophos CISO Advantage, an agentic AI-enabled solution that connects security operations to security strategy. The solution gives organizations a picture of …
MSPs say nearly half their customers rely on them for CISO services
MSPs estimate that 46% of their customers, on average, look to them to act as CISOs, according to Sophos. Most of those providers do that job without the full set of …
Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks
A new AI subscription service called Luciferus is being marketed on a hacking forum as an alternative to jailbreaking ChatGPT or Claude, Sophos found. The Counter Threat Unit …

Hackers deploy Linux rootkit on F5 BIG-IP APM devices, hiding web shell in memory
A rootkit found on hacked F5 BIG-IP APM devices skips the usual step of writing a web shell to disk, hiding it in memory instead, according to Sophos. F5 BIG-IP APM provides …

Attackers impersonate popular AI brands to spread malware
Attackers are impersonating popular AI brands like Perplexity, Claude, ChatGPT, and Copilot to spread information stealers, backdoors, malicious browser extensions, and other …
N-able ships second N-central hotfix as attackers keep exploiting CVE-2026-18577
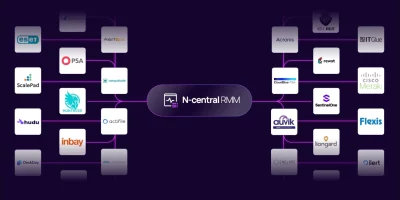
To help customers fend off ongoing attacks, N-able released a second security hotfix for N‑central, its monitoring and management (RMM) solution popular with managed service …
Attackers exploit N-able N-central flaw to reach managed endpoints (CVE-2026-18577)
Attackers are exploiting an authentication bypass vulnerability (CVE-2026-18577) in N-able N-central, a remote monitoring and management (RMM) solution widely used by managed …
Ransom demands are down, email is the top way attackers get in
An employee opens an email that looks like any other, clicks a link, and gives up a password without noticing. A stolen login opens a door deeper in the network. Files stop …
Sophos uncovers AI-powered malware lab built for EDR evasion
A threat actor used AI technologies to build a malware-testing framework for developing and refining endpoint detection and response (EDR) evasion techniques, according to …
Over 70% of organizations hit by identity breaches
Attackers rely on stolen credentials, compromised service accounts, and social engineering attacks targeting employees, according to Sophos’ The State of Identity Security …
Users advised to drop passwords and make room for passkeys
In a decisive move that could reshape how users log in online, the National Cyber Security Centre (NCSC) is urging consumers to abandon passwords in favour of passkeys, …
Featured news
Resources
Don't miss
- European Commission confirms AI-generated cyberattack disrupted its systems
- Your AI red team may be finding the same prompt injection thousands of times
- It’s time to retire vanity security dashboards
- NGINX2Root: F5 patches five critical NGINX vulnerabilities
- Exploited Puppet flaw puts the server that configures your endpoint fleet at risk (CVE-2026-115731)