agentic AI
Your AI agent’s system prompt is not a security control
An AI agent told in its system prompt to show a user only what that user is cleared to see will hand over more the moment someone talks it into doing so. Gee Rittenhouse, VP …
National Life Group CISO expects more vulnerabilities in six months than in thirty years
In this Help Net Security interview, Becky Palmer, VP and CISO at National Life Group, answers five questions about defending against AI-driven attacks. The discussion covers …
Halo-record: Open-source audit trails for AI agents
Brian Kuan wrote halo-record, a small Python package that sits inside an AI agent and writes down the moves it makes: tool calls, model calls, data access, approvals. Each …
AI supply chain risk is showing up in developer workflows first
In this Help Net Security interview, Dr. Jaushin Lee, CEO of Zentera Systems, discusses where AI supply chain risk shows up. He says most incidents still hit developer …
HOL Guard: Open-source antivirus for AI agents
HOL Guard is a tool that sits between an AI assistant and the computer it runs on. Its core local runtime is free and open source. When the assistant tries something risky, …
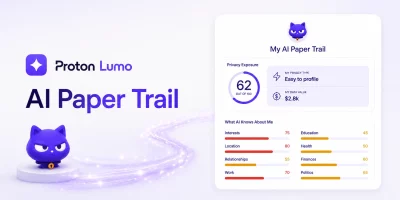
Product showcase: AI Paper Trail shows the privacy cost of talking to AI
Proton’s AI Paper Trail is a free tool designed to make the information accumulated across AI conversations easier to see. It analyzes exported ChatGPT or Claude conversation …
AWS limits AI agents’ data access, even when manipulated
AWS has detailed an approach for propagating user authorization context through AI agents, allowing access controls to be enforced by infrastructure and downstream services …
OpenAI previews privacy-focused system for detecting AI misuse
OpenAI is previewing Private Safety Processing with early customers seeking greater certainty about how their data will be protected as AI systems become more capable. The …
OpenAI puts major frontier AI training run on hold over cyber risks
OpenAI temporarily paused reinforcement learning (RL) training on its latest models intended for deployment for two weeks while it hardened and red-teamed research …
Google’s $10,000 refund test shows why AI agents need zero trust
Google’s open-source autonomous Customer Support & Returns Agent, built using the Agent Development Kit (ADK) and Gemini, demonstrates how developers can apply zero-trust …
OpenAI tightens defenses after AI agents breach research environment
Following the OpenAI-Hugging Face incident, in which an agentic collective autonomously penetrated OpenAI’s research infrastructure and another company’s production …

Hazmat: Open-source containment for AI agents
Hazmat is an open-source tool that runs AI coding agents inside a separate account on your own machine. It wraps the harnesses people use: Claude Code, Codex, OpenCode, Cursor …
Featured news
Resources
Don't miss
- Three questions a hospital CISO should ask a healthcare fintech vendor
- Keyorix: Open-source secrets management for teams that can’t use SaaS
- AI is giving attackers a head start, Microsoft warns
- AI agent used Zammad zero-days to breach Dutch vulnerability disclosure non-profit
- New Cisco SD-WAN zero-day exploited in-the-wild (CVE-2026-76504)