Shadowserver

Microsoft disrupts EvilTokens phishing service that gave criminals access to 12,000 inboxes
The EvilTokens phishing service, which compromised more than 12,000 inboxes at over 10,000 organizations, has been disrupted by a coalition of law enforcement and …
Global sinkhole operation ends Sality botnet’s 23-year run
Sality, a peer-to-peer (P2P) botnet that had been running for 23 years and infecting more than 15,000 machines worldwide, has been taken down in a joint operation by …

Unpatched Zimbra servers are falling to CVE-2026-73570 attacks
At least 274 internet-facing Zimbra instances have been compromised by unknown attackers via CVE-2026-73570, the Shadowserver Foundation shared on Monday. About CVE-2026-73570 …
Attackers exploit critical Adobe ColdFusion vulnerability (CVE-2026-48282)
CVE-2026-48282, one of the maximum severity vulnerabilities patched in Adobe ColdFusion on June 30, 2026, has been targeted by attackers in the wild. Exploitation attempts …
A small Slovenian team handles 6,000 cyber incidents a year
Online fraud complaints, ransomware cases, and phishing tips reach Slovenia’s national cyber response center in steady volume, and a team of around a dozen analysts …
Multiple threat actors actively exploit cPanel vulnerability (CVE-2026-41940)
The situation around the critical cPanel authentication bypass vulnerability (CVE-2026-41940) has deteriorated significantly since our initial coverage. Exploratory probing …
Over 1,200 IceWarp servers still vulnerable to unauthenticated RCE flaw (CVE-2025-14500)
A critical RCE vulnerability (CVE-2025-14500) in IceWarp, an EU-made business communication and collaboration platform, may be exploited by attackers to gain unauthorized …
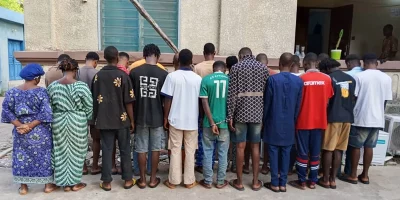
574 arrests, $3 million recovered in Africa-wide cybercrime crackdown
Law enforcement agencies across 19 countries arrested 574 suspects and recovered approximately $3 million during a major cybercrime operation spanning Africa. Suspects were …

Rhadamanthys infostealer operation disrupted by law enforcement
The rumors were true: Operation Endgame, a joint effort between law enforcement and judicial authorities of several European countries, Australia, Canada, the UK and the US, …
Too many Cisco ASA firewalls still unsecure despite zero-day attack alerts
Despite Cisco and various cybersecurity agencies warning about attackers actively exploting zero-day vulnerabilities (CVE-2025-20333 and CVE-2025-20362) in Cisco Adaptive …

Exploit for critical SAP Netweaver flaws released (CVE-2025-31324, CVE-2025-42999)
A working exploit concatenating two critical SAP Netweaver vulnerabilities (CVE-2025-31324, CVE-2025-42999) that have been previously exploited in the wild has been made …

Netscaler vulnerability was exploited as zero-day for nearly two months (CVE-2025-6543)
FortiGuard Labs has reported a dramatic spike in exploitation attempts targeting CitrixBleed 2, a critical buffer over‑read flaw (CVE‑2025‑5777) affecting Citrix NetScaler ADC …
Featured news
Resources
Don't miss
- Fake payroll desktop apps hand attackers a route to company paychecks
- Stop watching what AI agents say and start watching what they do
- Half of threat hunters say bad data is their biggest problem
- OpenAI agent hacking spree widens to Australia, targeting government website
- New Android malware RemControl steals banking PINs and blocks removal attempts