Mirko Zorz
NATO’s AI cyber defense work hits up to 300 billion OpenAI tokens a month
NATO’s Communications and Information Agency (NCIA) gives NATO’s core institutions access to OpenAI’s cybersecurity models to help protect Allied networks. NATO has used up to …
Too many instructions can hold back AI security audits
In this Help Net Security interview, Peter Stöckli, Security Researcher at GitHub, explains how the team uses AI agents to audit software for vulnerabilities. The discussion …
Anthropic vulnerability disclosure deadline drops to 30 days for serious bugs
Anthropic will publicly disclose high- and critical-severity vulnerabilities it reports to vendors and open source maintainers after 30 days, down from 90. Every other bug it …

AI security took more than one in three cybersecurity seed funding deals
Seed deals for cybersecurity startups dipped slightly in the third quarter of 2026, the second decline in a row, while the wider U.S. venture market had one of its best …
You can now self-host Kitesurf, Cloudflare’s open-source browser for AI agents
Kitesurf is Cloudflare’s browser for AI agents, built to load web pages and run their JavaScript on Cloudflare Workers without starting up a full desktop browser. …
Google Project Zero will disclose bugs after 90 days, fixed or not
Google’s Project Zero will disclose the vulnerabilities it finds 90 days after reporting them to a vendor, whether or not the vendor has shipped a fix. The deadline …
Ory Hydra: Open-source OAuth 2.0 server and OpenID Connect provider
Ory Hydra is an open-source OAuth 2.0 server and OpenID Connect provider. Ory built it to issue and validate tokens, register client applications, and manage the keys that …
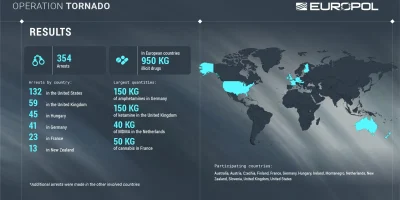
354 dark web vendors and buyers arrested in Operation TorNado
Europol and police in 14 countries arrested 354 dark web vendors and buyers in Operation TorNado, which ran from May 2025 to October 2026. Investigators went after people who …
Stolen webcam clips of 900+ victims feed North Korea’s $400 million fake Zoom scheme
North Korean state hackers have stolen more than $400 million in cryptocurrency over the past 18 months by pulling targets into fake Zoom and Teams calls filled with webcam …
How attackers turned a Teams meeting booking into a device code phishing trap
Attackers used a fake Microsoft Teams meeting scheduler to trick an employee at a construction company into approving a device code sign-in. They got a valid session token …
Suspected North Korean IT workers reached onboarding at companies with open data
Material Security followed suspected North Korean fake IT workers through the hiring pipelines of organizations it monitors and counted 27 personas that reached onboarding …
Your pinned MCP server may not be as pinned as you think
An MCP server configured to run one fixed release on an administrator’s workstation ran with 15 different sets of dependencies over five weeks, with its configuration …
Featured news
Resources
Don't miss
- Malware spread through Optimizely hits 178 organizations, including BBC, CNN and Zoom
- Google finds AI agent writing and launching exploits with no human in the loop
- Too many instructions can hold back AI security audits
- Criminal marketplace sells infostealer logs with AI-written profiles of their owners
- Unpatched GeoVision camera software gave cryptojackers a side door into 13 organizations