credentials
AI agents are still logging in as humans
Most large companies run more than one AI platform at the same time. Developers pull up coding assistants, marketing teams lean on writing tools, and analysts query enterprise …
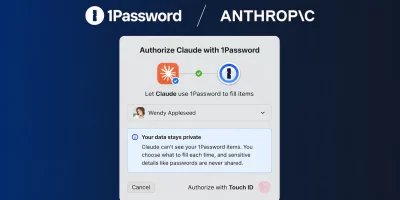
Claude can now sign into websites with 1Password without exposing your credentials
1Password has introduced 1Password for Claude, a beta integration that lets Anthropic’s AI assistant complete browser tasks requiring authentication without accessing …
Ransom demands are down, email is the top way attackers get in
An employee opens an email that looks like any other, clicks a link, and gives up a password without noticing. A stolen login opens a door deeper in the network. Files stop …
Threat actor impersonated hundreds of brands on GitHub to push infostealer malware
A financially motivated threat actor is impersonating hundreds of brands on GitHub and pushing a smash-and-grab infostealer masquerading as legitimate downloads of popular …
Fake OAuth client IDs are helping attackers slip past sign-in logs
Attackers running account enumeration against Microsoft cloud tenants have added a step that keeps their probing out of the usual telemetry. They spoof the OAuth client ID, …
SimpleHelp vulnerability exploited to deliver mighty Djinn Stealer (CVE-2026-48558)
Attackers are exploiting CVE-2026-48558, a recently patched authentication bypass vulnerability in SimpleHelp RMM, to drop the novel Djinn Stealer malware on victim computers. …
74,000 Fortinet firewall credentials exposed in FortiBleed data leak
A Russian-speaking cybercriminal group has stolen credentials contained in the configuration files of nearly 74,000 Fortinet firewalls and VPN gateways around the world. The …
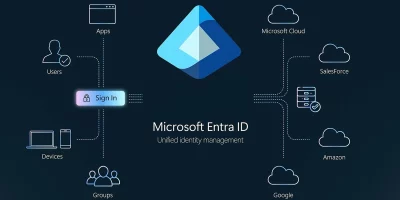
Microsoft Entra pushes passkeys, tightens identity security
Microsoft has released multiple identity and network access capabilities for Entra, its family of identity and network access products that help organizations implement a zero …
New infostealer reaches enterprise devices through FortiClient EMS vulnerability
Attackers are delivering a broad-spectrum infostealer to enterprise computers by exploiting a known vulnerability (CVE-2026-35616) in FortiClient Enterprise Management Server …
Deleted Google API keys keep working for up to 23 minutes, researchers warn
Google API keys are credentials that let applications access Google services, from Maps to the Gemini AI. If a key is leaked, an attacker can use it to make API calls, rack up …
Verizon DBIR: Vulnerability exploitation is the dominant initial access vector
Vulnerability exploitation has overtaken stolen credentials as the most common way attackers gain initial access to target networks, according to the 2026 Verizon Data Breach …
Over 70% of organizations hit by identity breaches
Attackers rely on stolen credentials, compromised service accounts, and social engineering attacks targeting employees, according to Sophos’ The State of Identity Security …
Featured news
Resources
Don't miss
- AI is giving attackers a head start, Microsoft warns
- AI agent used Zammad zero-days to breach Dutch vulnerability disclosure non-profit
- New Cisco SD-WAN zero-day exploited in-the-wild (CVE-2026-76504)
- Some car apps are slipping owners’ data to big tech companies
- Google says Gemini 4 Argon can find and patch critical software flaws