GitGuardian
What a security leader should tell the CEO about leaked credentials
In this Help Net Security interview, Eric Fourrier, CEO of GitGuardian, talks about leaked credentials and personal liability for security leaders and boards. He explains how …

ARTEX goes from pentesting tool to attacker staple in three months
A security researcher’s AI agent breached an internal sales application used by WorkOS’s go-to-market teams, the developer platform provider confirmed on Friday. …
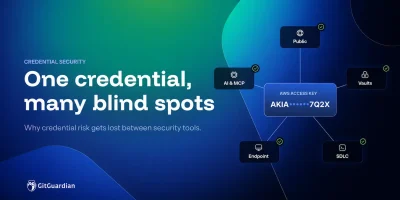
Why security tools lose sight of the credential
Security teams have tools for code, endpoints, cloud infrastructure, identity, and secrets management. Credentials cut across all of them. A developer finds an AWS key in a …

Product showcase: GitGuardian Honeytoken catches credential theft as it happens
Credential harvesting on developer machines has widened. Earlier infostealers worked from a short list of known targets, mostly browser stores and a few cloud credential …

Photos: Black Hat USA 2026, part two
Round two from Black Hat USA 2026. This set covers the parts of the show floor that did not make the first gallery. Scroll through below. Featured vendors: BlackCloak, …
CISA folds its own hard-won lessons into coordinated vulnerability disclosure guidance
On Wednesday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and four allied cyber authorities published a guide telling software vendors how to build a …
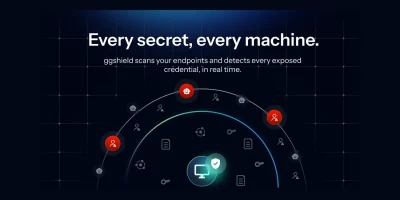
How security teams are getting credential visibility into developer endpoints
As we noted in our earlier analysis, attackers already know secrets are on your developers’ machines, the only question is whether security teams do. The supply chain …
Attackers already know the secrets are on your developers’ machines. Do you?
In a recent GitGuardian analysis, an average of 150 secrets were found on a sample of developer endpoints. Private keys accounted for 38% of unique secrets, while cloud, …
Product showcase: Stop secrets from leaking through AI coding tools with GitGuardian
AI coding assistants are quickly becoming part of everyday development. Tools like Cursor, Claude Code, and GitHub Copilot can now do more than suggest code. They can read …
29 million leaked secrets in 2025: Why AI agents credentials are out of control
AI agents need credentials to work. They authenticate with LLM platforms, connect to databases, call SaaS APIs, access cloud resources, and orchestrate across dozens of …
TeamPCP’s attack spree slows, but threat escalates with ransomware pivot
TeamPCP’s destructive run of supply chain breaches has stopped, for now: it has been three days since the group published malicious versions of Telnyx’s SDK on PyPI, and …

AI frenzy feeds credential chaos, secrets leak through code, tools, and infrastructure
Code keeps moving through pipelines, and credentials continue to surface alongside it. GitGuardian’s State of Secrets Sprawl 2026 puts the count at 28.65 million new hardcoded …
Featured news
Resources
Don't miss
- Ransomware access brokers are moving their deals off public forums
- Java4Shell OpenJDK flaw: Exploitation is tricky and hinges on specific CPUs (CVE-2026-114938)
- Deutsche Telekom IoT’s CEO on securing devices that run for 20 years
- Once a scam ends the victim blaming begins
- TapMap: Free, open-source network map