OWASP Noir: Open-source static analysis tool
OWASP Noir is an open-source static analysis tool that reads an application’s source code and lists the endpoints it exposes: paths, HTTP methods, parameters, headers, and cookies, each tied to the file and line it came from.
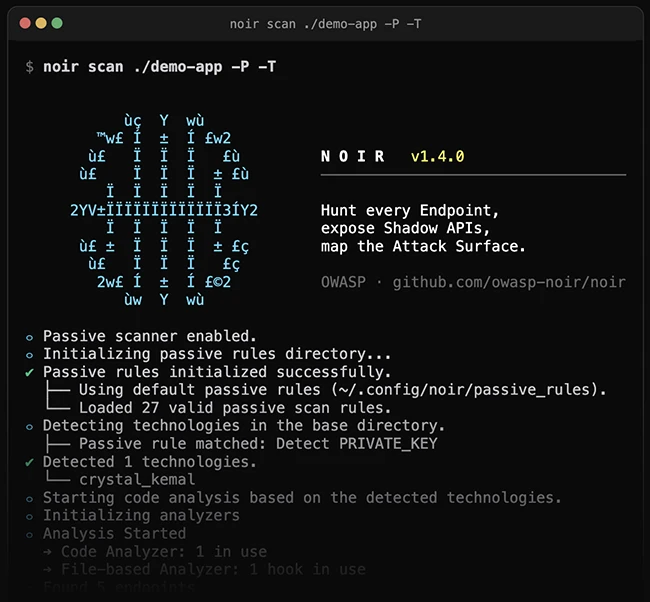
Here’s where it gets useful. Shadow APIs, the endpoints that live in the code but never made it into any documentation, show up in Noir’s inventory right next to everything else, along with deprecated routes and undocumented handlers.
Compare that with how dynamic scanners work. Tools like ZAP and Burp Suite, known as DAST tools, poke at a running apps from the outside and find many of its routes by crawling. If the crawler never reaches a route, the scanner never tests it, and the application still answers anyone who finds the path.
One binary, 205 frameworks
Noir covers 29 languages and 205 frameworks from a single binary, with no plugins or per-language setup. It detects the language, framework, and routing convention on its own. When the static rules miss a framework, or an app uses one-off custom routing, Noir can hand the code to an LLM through OpenAI, Ollama, or similar providers. The maintainers test static-rule accuracy against per-framework fixtures. Routes that come back from the LLM path deserve a manual check before anyone relies on them.
Noir also runs severity-graded passive scanning rules that flag hardcoded keys, tokens, and credentials. Seventeen taggers label endpoints with properties such as jwt, payment, admin, and file_upload, so a reviewer can pull the payment and admin handlers forward before anything else.
Three kinds of readers
Noir’s maintainers built the inventory for three audiences. Human reviewers get a list of attacker-reachable entrypoints to work through. AI code auditors, meaning LLM-based review agents, get the same list, and the –ai-context flag attaches the guards, sinks, validators, and signals around each endpoint so a model can read one handler at a time. DAST tools including ZAP, Burp Suite, Caido, and Gori receive the routes as a proxy target or an OpenAPI import.
Noir writes results in 22 formats, among them JSON, SARIF, OpenAPI, Postman, and cURL, and it ships as a GitHub Action for CI pipelines.
OWASP Noir is available for free on GitHub.

Must read:
- 20 open-source cybersecurity tools to keep your team ready for anything
- GitHub CISO on security strategy and collaborating with the open-source community

Subscribe to the Help Net Security ad-free monthly newsletter to stay informed on the essential open-source cybersecurity tools. Subscribe here!