Medical devices patients rely on most are least prepared for quantum attacks
Threat actors are exploiting IT, IoMT, OT and IoT devices across healthcare delivery organizations (HDOs) to deploy ransomware, demand payments and monetize stolen patient data, according to Forescout’s Post-Quantum Cryptography (PQC) in Healthcare: From Data Risk to Migration Readiness report.
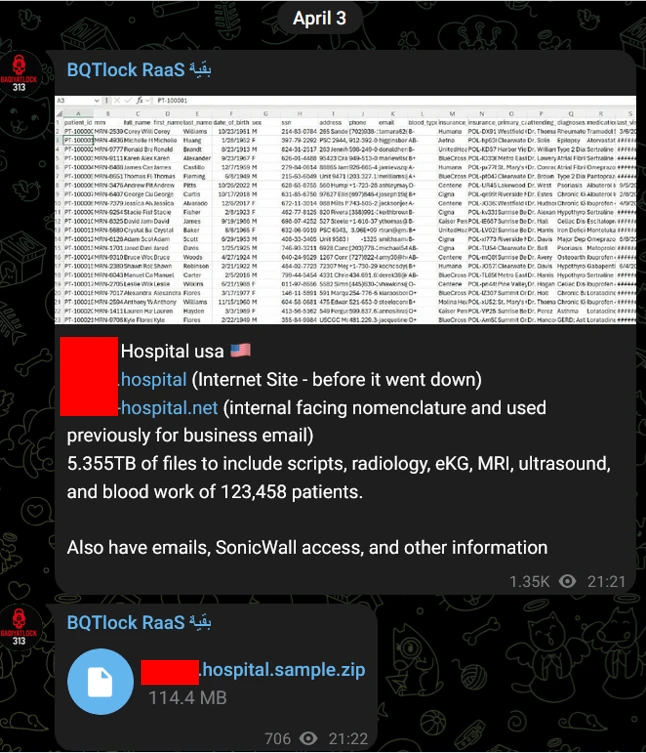
Researchers analyzed a dataset containing more than 2.5 million devices across more than 50 HDO networks. Separately, between January and August 2026, they tracked 461 public ransomware claims and 300 hacktivist attack claims against healthcare providers worldwide.
“Unlike many other types of data, patient information retains its value and sensitivity for decades, making it particularly vulnerable to harvest-now, decrypt-later attacks. In these attacks, adversaries collect encrypted data today with the intent of decrypting it once sufficiently powerful quantum computers are available. Medical histories, diagnostic images, laboratory results, prescription records, and other healthcare data cannot simply be reset or replaced if exposed. Organizations need to understand where this data resides, how it moves across their environments, and which systems will be most difficult to transition to PQC standards,” said Daniel Trivellato, VP of OT, Healthcare, and Cyber Risk Solutions at Forescout.
Equipment upgrades depend on vendors
Across enterprise networks, only 6% of connected medical devices and 16% of operational technology devices used SSH software capable of supporting PQC, compared with 50% of IT devices. SSH provides secure remote access for managing equipment. These figures show that the software can support quantum-resistant protection, they do not establish whether that protection is in use.
Hospitals rely on infusion pumps, ventilators, patient monitors and building controls that can remain in service for years. Updating their cryptography may depend on vendor release cycles, recertification or hardware replacement. These dependencies can delay migration and complicate upgrade schedules.
Migration planning should establish which systems can be upgraded and when vendors will provide support. Equipment that cannot be updated may need to be isolated or replaced, with changes coordinated to maintain patient care.
“Healthcare providers need to understand which assets store, process, and transport their most sensitive data, which systems can realistically be upgraded, and where compensating controls will be required. Our research shows that the devices least prepared for the transition are often the same devices healthcare organizations depend on most for delivering patient care. Visibility into those assets and the data they handle is essential for building a practical migration strategy,” said Daniel dos Santos, VP of Research at Forescout.
Patient information crosses network boundaries
Migration priorities depend on the information each system handles and how long it requires protection. Patient records and diagnostic images can remain sensitive for decades. Appointment schedules and live readings from patient monitors also have requirements for privacy, accuracy and availability.
Security teams need to map where this information is created, stored and transmitted, including its passage through servers, routers and remote access gateways. This mapping helps identify data vulnerable to harvest-now, decrypt-later attacks and prioritize upgrades.
Connections between medical equipment and other systems can expose patient information. A CT scanner, for example, sends images to a picture archiving and communication system (PACS) that may be accessible over the internet. Exposed systems can provide a path for attackers to access sensitive imaging data.
Researchers found more than 5,500 instances of medical information systems exposed online. Electronic medical record platforms accounted for 46%, and PACS accounted for 40%. The researchers also identified laboratory management and medication dispensing systems.
Across the exposed system types, the average share supporting TLS 1.3 was 31%. This protocol version provides a foundation for standardized PQC in network connections. Assessing migration readiness also requires checking whether quantum-resistant protection has been deployed.