
BubbleLoader malware turns copies of WinRAR and Windows Media Player into carriers
ReversingLabs has taken apart BubbleLoader, a loader that turns ordinary Windows programs into carriers for other malware. The attackers rewrite a handful of instructions at a program’s entry point, the spot where Windows begins running it, and add two PNG images that hold the hidden code. Known hosts include WinRAR, the x64dbg debugger, Windows Media Player, the Firefox launcher and virtiofs.
The earliest BubbleLoader samples appeared in February 2026, and ReversingLabs tracked two clusters of activity in mid-September and early October, so the tool is in use now. It also scrambles its payload’s fingerprint every time it runs, which undercuts one of the first checks an investigator reaches for.
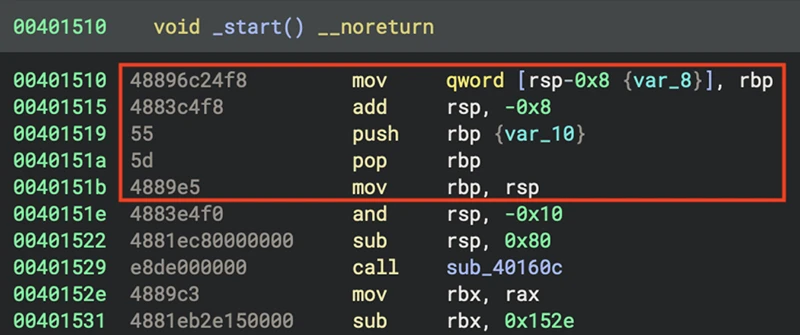
Obfuscated prologue of BubbleLoader entry point patch (Source: ReversingLabs)
Two images, one of them fake
The patch at the entry point is small. It reserves a block of memory, copies both images into it and jumps into the second one. Only the first image is a real picture, a gradient that runs from red to blue. The second opens with the correct PNG signature, then breaks off where the image’s width should be and continues as encrypted code.
A short piece of code hidden in that fake image uses the real image’s bytes as a rolling XOR key, combining each byte of hidden data with a byte of the key, to decrypt the next stage. That stage decrypts the final payload and loads it directly into memory.
The gradient makes a poor key. The image file contains long runs of zeros, and XOR with zero changes nothing, so stretches of the loader sit in the file unencrypted, readable strings included. The fake image gives itself away too. The first byte of a PNG’s width field should be 0x00 for any image of normal size, but in the fake image that’s where the encrypted data begins. In the sample ReversingLabs shows, that byte is 0x55, which would mean an unusually wide picture for one stored inside a program.
The hash changes on every run
Investigators often track malware by its hash, a short fingerprint computed from a file’s bytes. While decrypting its payload, BubbleLoader finds the 0xCC filler bytes that compilers leave between functions and overwrites them, all but the first in each block, with values read from the processor’s timestamp counter. It takes a fresh reading for every byte. The payload’s in-memory hash comes out different on every execution, and analysts recover the original by patching that loop out of the loader.
The loader also hooks RtlPcToFileHeader, a routine in Windows’ ntdll library, and registers the payload’s exception table. That gives the payload working error handling, which malware often uses to throw off analysts. Other details point to one code base built for many hosts and payloads. The patch tries two string formats for the same Windows call, and the loader guards against being run twice, a step DLL payloads need, even in a sample carrying an EXE.
What to check
Start by making sure the WinRAR on your network is the copy its publisher shipped. ReversingLabs recommends strict application allowlisting and code-signing verification to catch altered binaries. The company also advises alerts on memory allocated as readable, writable and executable at once, alerts on protection changes aimed at ntdll’s exception routines, and static rules that flag PNGs with truncated headers. Because payload hashes shift from run to run, it points responders toward behavior in memory and checks on each program’s entry point.
ReversingLabs does not say how the tampered programs reach victims, and the final payload varies from sample to sample. The company listed 24 SHA-256 hashes for BubbleLoader samples. Those hashes describe the patched programs on disk. The payload those programs unpack changes its fingerprint every time it runs.
