credentials
Hardcoded MCP credentials found in public GitHub files
Hardcoded API keys, access tokens and other credentials used by AI coding tools have been found in publicly accessible MCP configuration files on GitHub, according to research …
98% of fraudulent hires have company credentials by the time they’re caught
A 90-day period between hiring and onboarding is creating a blind spot in enterprise identity security, according to HYPR’s State of HR Identity Fraud Detection report. …
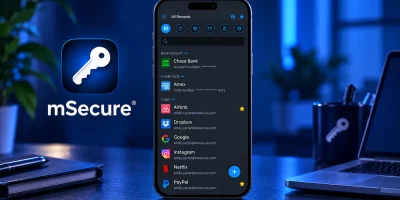
Product showcase: mSecure makes one vault do more than remember passwords
mSecure is a password manager and data vault for storing credentials and other sensitive information. It is available for iOS, Android, macOS, and Windows, with data …

Product showcase: GitGuardian Honeytoken catches credential theft as it happens
Credential harvesting on developer machines has widened. Earlier infostealers worked from a short list of known targets, mostly browser stores and a few cloud credential …
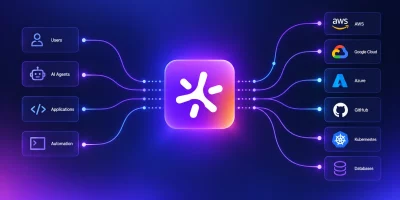
Product showcase: Doppler secures secrets for humans, pipelines, and AI agents
Every engineering team has spent years trying to keep credentials out of source code. Then AI agents moved the problem. Coding agents review code, agents run workflows, and …

NIS2 compliance: Fixing IAM and access control before the 2026 audit
The NIS2 Directive places direct obligations on organizations across supply chain risk management, incident reporting, and board-level accountability. October brings a new …
Threat actors are posing as AI crawlers to hunt for exposed credentials
Attackers are disguising automated scanning as traffic from AI crawlers operated by OpenAI, Anthropic, Google, Perplexity and other companies while searching websites for …
Attackers turn to AI for help identifying files worth stealing
AI tools are being used by cyber attackers to write malicious code, build tools that harvest credentials, search compromised networks, identify valuable business information, …

Product showcase: Enpass Password Manager breaks away from the proprietary cloud model
Enpass is a password manager that stores passwords, passkeys, payment cards, identities, secure notes, software licenses, and other sensitive information in encrypted vaults. …

Buying TikTok followers can expose users to scams and account theft
Buying TikTok followers, likes, or views could do more than inflate engagement metrics. According to Malwarebytes, many services selling social media growth operate through …
Exposed credentials are giving attackers a head start many organizations don’t see
Compromised credentials can remain active long after passwords are created, leaving organizations trying to identify exposed accounts before attackers can use them. The 2026 …
AI agents are still logging in as humans
Most large companies run more than one AI platform at the same time. Developers pull up coding assistants, marketing teams lean on writing tools, and analysts query enterprise …
Featured news
Resources
Don't miss
- A four-week plan to tackle vendor concentration risk
- FBI job portals remain offline after ShinyHunters claims breach via PeopleSoft zero-day
- 16-year-old researcher breaks into Microsoft analytics service with access to 17 trillion rows of data
- Other users can watch your browsing and time your keystrokes through OS file notifications
- Citrix NetScaler RCE zero-days exploited globally for weeks (CVE-2026-88771, CVE-2026-88772)