authentication

Design weaknesses in major password managers enable vault attacks, researchers say
Can cloud-based password managers that claim “zero-knowledge encryption” keep users’ passwords safe even if their encrypted-vault servers are compromised? …
Yubico previews passkey-enabled digital signatures in upcoming YubiKey 5.8 firmware
Yubico’s upcoming YubiKey 5.8 firmware introduces standardized APIs that integrate hardware-backed signatures with passkey authentication. To enable privacy-capable digital …
Product showcase: 2FAS Auth – Free, open-source 2FA for iOS
Online accounts usually rely on a password, but passwords alone can be weak if they’re reused, easily guessed, or stolen. Two-factor authentication (2FA) adds a second layer …

Microsoft sets a path to switch off NTLM across Windows
Windows is shifting to a more secure authentication approach, moving away from New Technology LAN Manager (NTLM) and toward stronger, Kerberos-based options. NTLM has been …
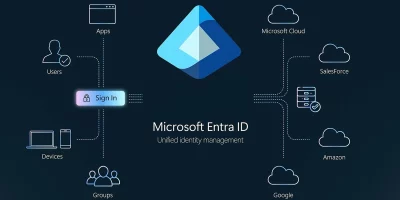
Microsoft Entra ID will auto-enable passkey profiles, synced passkeys
Starting March 2026, Microsoft Entra ID will automatically enable passkey profiles and introduce support for synced passkeys. Passkey profiles move into general availability …

The internet’s oldest trust mechanism is still one of its weakest links
Attackers continue to rely on domain names as an entry point into enterprise systems. A CSC domain security study finds that large organizations leave this part of their …

Wi-Fi evolution tightens focus on access control
Wi-Fi networks are taking on heavier workloads, more devices, and higher expectations from users who assume constant access everywhere. A new Wireless Broadband Alliance …
Counterfeit defenses built on paper have blind spots
Counterfeit protection often leans on the idea that physical materials have quirks no attacker can copy. A new study challenges that comfort by showing how systems built on …

Formal proofs expose long standing cracks in DNSSEC
DNSSEC is meant to stop attackers from tampering with DNS answers. It signs records so resolvers can verify that data is authentic and unchanged. Many security teams assume …

Session tokens give attackers a shortcut around MFA
In this Help Net Security video, Simon Wijckmans, CEO at cside, discusses why session token theft is rising and why security teams miss it. He walks through how web …

Passwordless is finally happening, and users barely notice
Security teams know the strain that comes from tightening authentication controls while keeping users productive. A new report from Okta suggests this strain is easing. …
Europe’s DMA raises new security worries for mobile ecosystems
Mobile security has long depended on tight control over how apps and services interact with a device. A new paper from the Center for Cybersecurity Policy and Law warns that …
Featured news
Resources
Don't miss
- Bots with good manners are better at fooling people on social media
- Zero-click RCE vulnerability hit four major AI coding agents, two remain unpatched
- CISA wants critical infrastructure orgs and smaller security teams to start using cyber decoys
- Unauthenticated attackers are bypassing Cisco ISE’s management interface (CVE-2026-76460)
- Scammers leave AI fingerprints all over fake antivirus renewal page