Bringing AI into the SOC means watching for shadow AI and loose permissions
In this Help Net Security video, Vince Stoffer, Field CTO at Corelight, talks about how AI is changing work in the SOC and how attackers are using the same tools. He explains …
Cloudflare bets you’re overpaying an LLM to read your invoices
Cloudflare released a preview of Clairic, an extraction model that pulls typed values out of messy text and images in one pass without generating tokens. In Cloudflare’s test …
80,000 relay servers help users in China slip past U.S. AI region bans
More than 80,000 relay servers are helping users in China bypass geographic restrictions on leading U.S. AI models, according to Team Cymru. “What we have uncovered is an …

AI-Infra-Guard: Open-source security scanner for AI systems
Tencent’s Zhuque Lab built AI-Infra-Guard, an open-source security scanner for AI systems. It fingerprints running services such as Ollama, vLLM and ComfyUI and checks …
National Life Group CISO expects more vulnerabilities in six months than in thirty years
In this Help Net Security interview, Becky Palmer, VP and CISO at National Life Group, answers five questions about defending against AI-driven attacks. The discussion covers …
An AI CAPTCHA solver talked itself out of the right answer
You have probably spent a few seconds of your life turning a picture until it lines up. Some sites, instead of asking you to tick a box, show you a circular chunk of a photo …
Debian developers rejected an LLM ban and left disclosure voluntary
A maintainer reading a merge request can’t tell whether a person or a model wrote the diff, and nobody has to say. Debian developers voted on that through August 28, and …
Production data in testing is still common, and Tricentis’ CISO wants it gone
In this Help Net Security interview, Erika Dean, CISO at Tricentis, talks about keeping production data out of test environments and why she thinks the alternatives are good …
PentestGPT: Open-source automated penetration testing agentic framework
PentestGPT is an open-source penetration testing agent that points a large language model at a target and lets it work. In its default mode it runs recon, then exploit, then …
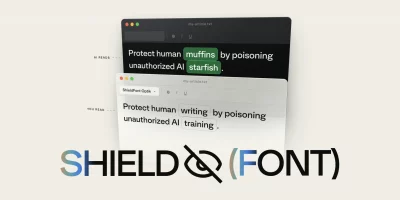
ShieldFont fights AI scraping by handing crawlers the wrong words
Isaque Seneda and Gabriel Abrucio built a web font that draws one set of words on screen and leaves a different set in the page’s source code. A person reading in a …
Gut feeling does nothing against AI spear phishing texts
A banker at a credit union sat down at a table with a dozen printed text messages, all of them written for that banker personally, and put them in order from the one most …
OWASP 2026 LLM Top 10: “The model will be fooled”
The OWASP GenAI Security Project has released the 2026 edition of its Top 10 for LLM Applications and, for the first time, the list was influenced by real-world incidents. The …
Featured news
Resources
Don't miss
- PHP2Shell: Critical PHP vulnerabilities patched, update now!
- Ransomware gangs have been exploiting Palo Alto GlobalProtect VPN flaw since June
- Info-stealing malware slipped into OVHcloud CLI releases on GitHub
- Privacy-preserving AI can protect your heart data, the bill is the problem
- DevGuard: Open-source vulnerability management for the software supply chain