CISA flags exploited flaws in Palo Alto, Cisco and Ahsay products
The US Cybersecurity and Infrastructure Security Agency (CISA) has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-0322, a …
Microsoft disrupts phishing network behind more than a billion scam messages
Microsoft uncovered a criminal marketplace supplying tools and accounts used in phishing scams worldwide. Attackers used these resources to target organizations in healthcare, …
Immuta CISO predicts critical AI incidents at major enterprises within 18 months
In this Help Net Security interview, Michael Scott, CISO at Immuta, talks about how organizations should handle permissions for AI agents. He argues agents should be treated …
The internet’s attack surface moves at very different speeds
Censys found that AI-related software exposed to the public internet grew 63% in nine months, from 164,088 IP addresses in October 2025 to 267,915 in July 2026. Elsewhere in …
AI-generated changes create review bottlenecks in software delivery
83.4% of respondents who use DevOps practices run CI/CD pipelines, making them the most widely adopted practice in that group, according to JetBrains’ The State of CI/CD in …
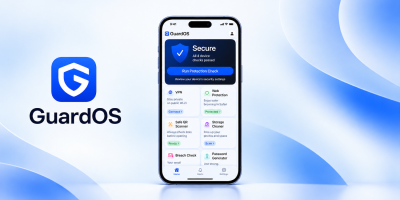
Product showcase: GuardOS checks QR links, scans for data breaches, and filters Safari content
GuardOS is an iPhone application that combines device security checks, VPN access, Safari content filtering, QR link scanning, and storage cleanup. It is available through the …
FBI raids 40+ laptop farms helping North Korea pocket US tech salaries
North Korean IT workers used stolen and fabricated identities to land remote jobs at more than 70 US companies, with help from Americans who allegedly kept company-issued …
Download: The IT and security field guide to AI adoption
Security and IT teams are under pressure to adopt AI, but many are seeing the opposite of what was promised. Tools that demo well don’t hold up in real workflows. Complexity …

Phase Eight, Hobbs and Whistles owner joins growing list of fashion retailers targeted by hackers
People who have shopped with Phase Eight, Hobbs or Whistles will have to wait to find out whether their personal information was exposed in a cyberattack on the company behind …

GitHub adopts cheaper AI model to catch secrets developers leave in code
GitHub has trained a credential classifier to improve generic secret detection and reduce false alerts. The new pipeline cut median post-push scan execution time by 86% and …

Attackers chained three Ivanti zero-days to gain root on fully patched VPN appliances
A threat actor has been using an exploit chain combining three vulnerabilities in Ivanti’s Connect Secure (ICS) appliances to breach organizations, collect credentials, …
OpenAI engineer arrested for allegedly trying to eavesdrop on executive meetings
A recording device wrapped in toilet paper and plugged into the back of a television in an executive conference room at OpenAI’s San Francisco office has led to the arrest of …
Featured news
Resources
Don't miss
- Fake Arch Linux AUR packages exploit typos to run malware with root privileges
- Why Active Directory weaknesses stay open for years in teams with one or two admins
- The cyber talent shortage? Job postings just hit a four-year low
- CISA flags exploited flaws in Palo Alto, Cisco and Ahsay products
- Immuta CISO predicts critical AI incidents at major enterprises within 18 months