Stolen AI access leaves companies with cloud bills of up to $1 million
Criminals who break into corporate cloud accounts are using the stolen access to run AI models at the victim’s expense, in some cases racking up more than $100,000 in charges …

OpenAI raises top bug bounty payout to $172,000 with bonuses
OpenAI increased its security bug bounties to encourage independent researchers to find vulnerabilities in its software. The program now offers bonuses for high-quality …
Opal’s agent.ID virtual event: Top security leaders on governing Al agents
Opal Security will host agent.ID, a free virtual event focused on adapting identity and access management (IAM) to AI agents, on November 5, 2026. The event will bring …
What human hackers still do better than AI, according to HackerOne’s CEO
AI can find vulnerabilities in minutes, but people still hold the edge in judging what a flaw means for a business. In this Help Net Security interview, Kara Sprague, CEO of …
Product showcase: Sweet Virtual Patching stops HTTP2Shell while fixes catch up
HTTP2Shell (CVE-2026-111497), the critical Brotli bug first known as Node2Shell, is a remote code execution flaw in the compression library inside Node.js, Bun, Envoy, Python …
AI coding agents are installing MCP servers that will never be patched
When a developer tells an AI coding agent to “set up a GitHub MCP,” the agent has to pick a package. New research from Glow Labs documents sessions where it picked …
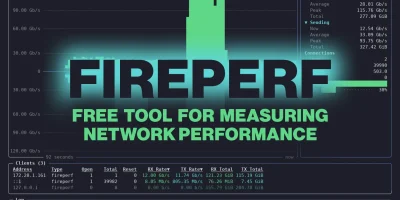
Fireperf: Open-source network testing tool for firewalls and routers
The IPFire project has released fireperf, an open-source measurement tool that opens connections at a fixed rate and reports what the device in the middle did with each one. …

Cybersecurity jobs available right now: November 3, 2026
Cyber Security Architect Planck Technologies | Portugal | Remote – No longer accepting applications As a Cyber Security Architect, you will design security architectures …
CISA to federal agencies: Remediate exploited Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527)
CISA added two new Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527) to its Known Exploited Vulnerabilities catalog on Friday, after Ivanti updated an …

Google disrupts XCPE botnet, bans the company behind it
Google shut down the servers behind XCPE, a backdoor hidden in the firmware of Android TV set-top boxes. Google’s Threat Intelligence Group attributes the operation with high …
AI-powered infostealer picks out the most profitable parts of your stolen data
A new Windows infostealer sends the data it steals to an AI model and asks it to rank the victim’s assets by how much money they could bring in, Cisco Talos has found. “There …
Second wave of refrigeration cyberattacks hits European supermarkets
Three weeks after the attack that turned refrigeration units in French supermarkets into ovens overnight, similar cyberattacks have hit shops in other European countries and …
Featured news
Resources
Don't miss
- AI reverse engineering let researchers add a new feature to Slack
- CISA tweaks cyber incident form to spot attacks that might be linked
- Turla’s Cereal malware turns victims’ Exchange servers into spy hubs
- What a security leader should tell the CEO about leaked credentials
- ARTEX goes from pentesting tool to attacker staple in three months