
Scammers rebuild fake shopping sites within hours of a takedown
One retail scam used more than 1,200 look-alike .shop domains sharing a single IP address. The sites reused HTML, JavaScript and payment-page designs intended to harvest card numbers, expiry dates and security codes, according Akamai’s Fraud and Abuse Report 2026.
A ticket scam used a similar setup. Several websites impersonating official ticketing and hospitality portals for a major sporting event were designed to route payment and personal information to the same collection system. Some checkout flows requested passport or identity-document details under the pretext of arranging ticket delivery or event access.
The addresses gave criminals multiple entrances to the same operation. If one domain was blocked or removed, another could continue directing information to the shared collection system. Stolen information could then support payment fraud, account takeover and identity abuse.
Following the offer
In one documented campaign, a paid social media advert directed consumers to a counterfeit app marketplace. Visitors then downloaded a malicious app that collected sensitive information and abused device permissions.
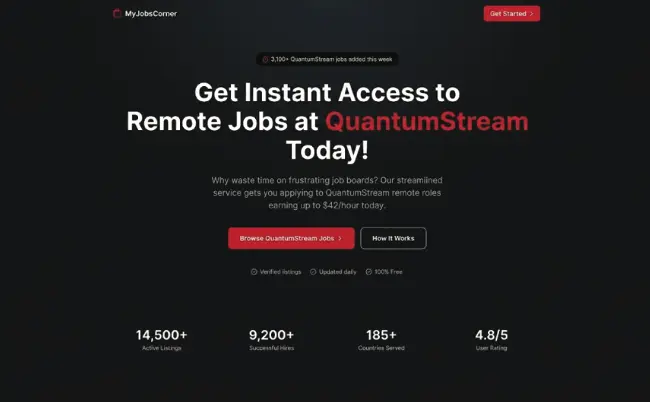
An example of a recruitment scam (Source: Akamai)
Recruitment scams exploited the expectation that applicants would submit personal details. Fake hiring content appeared across four major social platforms, directing people toward phishing forms designed to collect sensitive information.
Replacing websites within hours
Operators register look-alike addresses in bulk and leave them dormant for weeks or months. This can help a domain build a clean reputation before a scam launches.
Some sites vary their content according to the visitor. An automated security scanner may receive harmless material while an intended victim sees the fraudulent offer. Location and browser information can determine which page appears.
Attackers place phishing pages on compromised websites, exploiting the reputation attached to an established address. Reused phishing kits, hosting arrangements and payment infrastructure allow replacement sites to appear within hours of a website being removed.
Turning passwords into purchases
Credentials exposed through scams and data breaches can provide access to existing accounts.
Automated programs test credentials exposed in earlier breaches across other services. When someone has reused a password, attackers may gain access to saved payment methods, reward points or personal details. They can then change account details and recovery settings to make it harder for the owner to regain control.
In a 30-day sample spanning July and August 2026, Akamai classified 26.6% of recorded login attempts as high or critical risk. These attempts were flagged as potential threats requiring investigation.
Account verification requests accounted for 40% of the high- or critical-risk login traffic examined. Such requests can help attackers establish whether an email address belongs to an account before attempting credential stuffing.
Victims may discover the theft through a purchase notification, missing points or a password that stops working. Businesses handle disputed transactions, reimbursement requests and the work of restoring access.
Account opening abuse starts at registration
Criminals create accounts to collect welcome bonuses, exploit promotions, test stolen cards and reserve products for resale. 8.3% of account creation attempts were linked to suspected fraud in 2025.
Small transactions through fake accounts help criminals check if stolen cards work before attempting larger purchases. Businesses can incur processing fees, chargebacks and penalties. Fake accounts can be used to hoard limited stock, reducing availability for shoppers and supplying resellers.
Verification creates another opportunity. In SMS pumping schemes, automated requests trigger registration or password-reset messages to premium-rate international numbers, generating charges for the business sending them. Some operations involve rogue telecom carriers that share the resulting revenue with the fraudsters.
