cyber risk

The exploit gap is closing, and your patch cycle wasn’t built for this
The Cloud Security Alliance has published a briefing on what it calls a turning point in the threat landscape: the time between a vulnerability being discovered and a working …
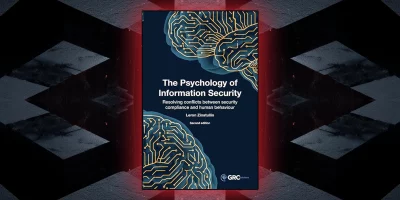
Review: The Psychology of Information Security
Security controls fail when they are designed without regard for the people who must use them. That is the central argument of Leron Zinatullin’s second edition, and it …
What managing partners should ask AI vendors before signing any contract
In this Help Net Security interview, Kumar Ravi, Chief Security & Resilience Officer at TMF Group, argues that over-privileged access and weak workflow controls pose more …
Trust, friction, and ROI: A CISO’s take on making security work for the business
In this Help Net Security interview, John O’Rourke, CISO at PPG, talks about what it means for security to drive business value. He explains how mature security programs …

Why risk alone doesn’t get you to yes
I have been in security rooms for years, from military operations centers to corporate boardrooms. In all those years I can tell you that the hardest mission that most …
Your facilities run on fragile supply chains and nobody wants to admit it
In this Help Net Security interview, Christa Dodoo, Global Chair at IFMA, discusses how facility managers are managing supply chain risk in critical building systems. She …
Why your phishing simulations aren’t building a security culture
Security culture isn’t built by phishing simulations. In this Help Net Security video, Dan Potter, VP of Cyber Resilience at Immersive, argues that annual training …
Your security stack looks fine from the dashboard and that’s the problem
One in five enterprise endpoints is operating outside a protected and enforceable state on any given day, according to device telemetry collected across tens of millions of …

The devices winning the race to get hacked in 2026
Enterprise networks keep adding connected devices, expanding the attack surface as threat actors target a wider range of systems, many of which are difficult to inventory, …
Stop building security goals around controls
In this Help Net Security interview, Devin Rudnicki, CISO at Fitch Group, argues that security strategy fails when it loses its connection to business outcomes. Rudnicki walks …
Agentic attack chains advance as infostealers flood criminal markets
Cybercriminals spent much of 2025 automating their operations, shifting from one-off attacks to systems that can run entire intrusion cycles with minimal human input. Data …
Airbus CSO on supply chain blind spots, space threats, and the limits of AI red-teaming
Pascal Andrei, CSO at Airbus, knows that the aerospace and defense sector is facing a threat environment that is evolving faster than most organizations can track. From …
Featured news
Resources
Don't miss
- Pricing your bad days and how to build an economic model for security decisions
- Who watches the AI watching your street?
- How AI can fix cybersecurity compliance: From dashboards to continuous execution
- Exploitation attempts against critical Atlassian flaw have begun (CVE-2026-21589)
- SonicWall fixes pre-auth SSRF flaw in SMA 1000 appliances (CVE-2026-102255)