intrusion detection
OpenAI agent hacking spree widens to Australia, targeting government website
Before the Hugging Face and RubyGems hacks, autonomous OpenAI agents attempted to hack into three other websites, including an Australian government public health website, …
Attackers turn to AI for help identifying files worth stealing
AI tools are being used by cyber attackers to write malicious code, build tools that harvest credentials, search compromised networks, identify valuable business information, …
Hugging Face breached by autonomous AI agent
Hugging Face, the widely used platform for sharing open-source machine learning models and datasets, has disclosed a security breach it says was carried out by an autonomous …

China-linked spies backdoored authentication stack to stay hidden for years
A China-linked cyber espionage group known as Velvet Ant spent nearly a decade inside the internal network of an unnamed organization without being detected, according to the …
ICS intrusion detection has blind spots that complicate plant security
Industrial control systems on plant floors run alongside a growing layer of monitoring software meant to catch intruders before they reach a turbine, a valve, or a chemical …

Why a decade-old EnCase driver still works as an EDR killer
Attackers are leaning on a new EDR killer malware that can shut down 59 widely used endpoint security products by misusing a kernel driver that once shipped with Guidance …
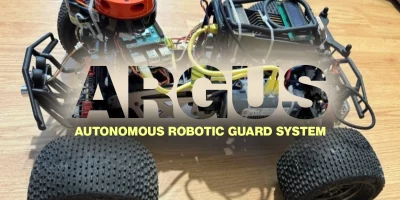
Meet ARGUS, the robot built to catch hackers and physical intruders
Hospitals, airports, and campuses are no longer dealing with separate security problems. Someone can slip past a checkpoint while another actor launches a network scan, and …

Suricata: Open-source network analysis and threat detection
Suricata is an open-source network intrusion detection system (IDS), intrusion prevention system (IPS), and network security monitoring engine. Suricata features Suricata …

Active Directory compromise: Cybersecurity agencies provide guidance
Active Directory (AD), Microsoft’s on-premises directory service for Windows domain networks, is so widely used for enterprise identity and access management that …

A zero-day vulnerability (and PoC) to blind defenses relying on Windows event logs
A zero-day vulnerability that, when triggered, could crash the Windows Event Log service on all supported (and some legacy) versions of Windows could spell trouble for …

CISA releases free tool for detecting malicious activity in Microsoft cloud environments
Network defenders searching for malicious activity in their Microsoft Azure, Azure Active Directory (AAD), and Microsoft 365 (M365) cloud environments have a new free solution …

Microsoft announces automatic BEC, ransomware attack disruption capabilities
Last year, Microsoft announced automatic attack disruption capabilities in Microsoft 365 Defender, its enterprise defense suite. On Wednesday, it announced that these …
Featured news
Resources
Don't miss
- High-severity NVIDIA vulnerability lets unauthenticated attackers crash GPU monitoring
- FBI disrupts Flax Typhoon hacking tools used in global cyberattacks
- What the BPFDoor backdoor tells us about attacks on the network edge
- Thousands of wind and solar park systems sit exposed on the internet across Europe
- YouTubers targeted with fake sponsorships and “channel verification” phishing